 56 minutes ago
239

The hacking group ShinyHunters claimed that the stash they stole from the FBI contains psychiatric and medical evaluation records of bureau personnel. If the claim is confirmed, this will become more than just an employee-data breach, but rather a long-term counterintelligence and identity risk debacle that cannot be remedied with a password reset.
Blood tests, mental-health notes, and a workforce mapped by ailment
The documents that have been discussed this week resemble clinical records more than a file on personnel. According to BBC News, which has reviewed a selection of the stolen documents, the medical records include blood and urine test results, doctors’ observations, allergies and other medical conditions, as well as the agents’ real names and addresses.
According to a review conducted by Reuters of other six documents, some records consist of mental health assessments before starting employment, electrocardiogram results, a document mentioning the applicant showed “signs of depression” in high school, and a paper indicating that the individual has taken aspirin on a daily basis and was allergic to certain substances.
Reuters partially confirmed some of the records based on credit bureau details, LinkedIn profiles, and information from an individual acquainted with the FBI assessments.
As Etay Maor, vice president of threat intelligence at Cato Networks, states in his interview with the BBC:
Passwords can be reset if stolen, but medical records cannot.
Why an FBI job portal held spy-grade identity data
The medical records highlight an already significant personnel-exposure issue. Cryptopolitan previously reported that Reuters examined a 5,000-line sample connecting identified FBI employees to intelligence, surveillance, and counterintelligence jobs, including operations in Russia and China. The cybercriminals claim that the full amount of stolen data is between two and three terabytes.
The FBIJobs.gov website contains a wealth of information on its applicants and employees. Moreover, ShinyHunters asserted that it also hacked internal systems, such as the FBI MedLink service and background-checking systems, but so far this claim has not been independently verified by Reuters. On Wednesday, the FBI stated that it was “actively and aggressively investigating” the matter while the cause remains unclear.
An extortion crew that skipped the ransom demand
ShinyHunters is not a new name. According to Huntress, it is a financially motivated operation that has been in existence at least since 2019 and has gained notoriety for stealing SaaS and cloud data on a huge scale while also using “pay or leak” extortion tactics.
This time, the group broke precedent. Instead of demanding money, it instead sought an apology from the FBI for a May notice that it had claimed insulted it, although it eventually rescinded that demand.
According to Cryptopolitan, FBIJobs.gov uses Oracle PeopleSoft technology and Google’s Mandiant linked ShinyHunters to the PeopleSoft hacks that took advantage of the CVE-2026-35273 vulnerability that Oracle assessed with a score of 9.8 out of 10. There is no evidence in the public domain that connects the vulnerability with the breach at this point in time.
Echoes of the 2015 OPM breach
Federal personnel records had caused such a level of damage before. According to the Government Accountability Office (GAO), the breach of the Office of Personnel Management (OPM) in 2015 compromised sensitive data of around 22 million federal employees and contractors. The GAO later discovered that the agency responsible for the majority of the federal background checks did not fully install the privacy controls in all the systems that it examined.
Eric O’Neill, a former FBI agent who established Nexasure AI, said to Reuters that the medical information elevates this event to a similar level, and may attract the attention of hostile intelligence services.
I would be shocked if Russian intelligence isn’t knocking on their door and saying, ‘We want that stuff, hand it over.
— Eric O’Neill, former FBI operative and founder of Nexasure AI, speaking to Reuters
The bill lands on everyone else
The breach will not move global markets on its own, but incidents like it keep raising security, compliance and insurance costs across industries. IBM’s 2026 breach study puts the global average cost at $4.99 million, up 12%, while AI-driven attacks rose 56%. Its X-Force index says exploitation of public-facing applications rose 44% and major supply-chain compromises have nearly quadrupled in five years.
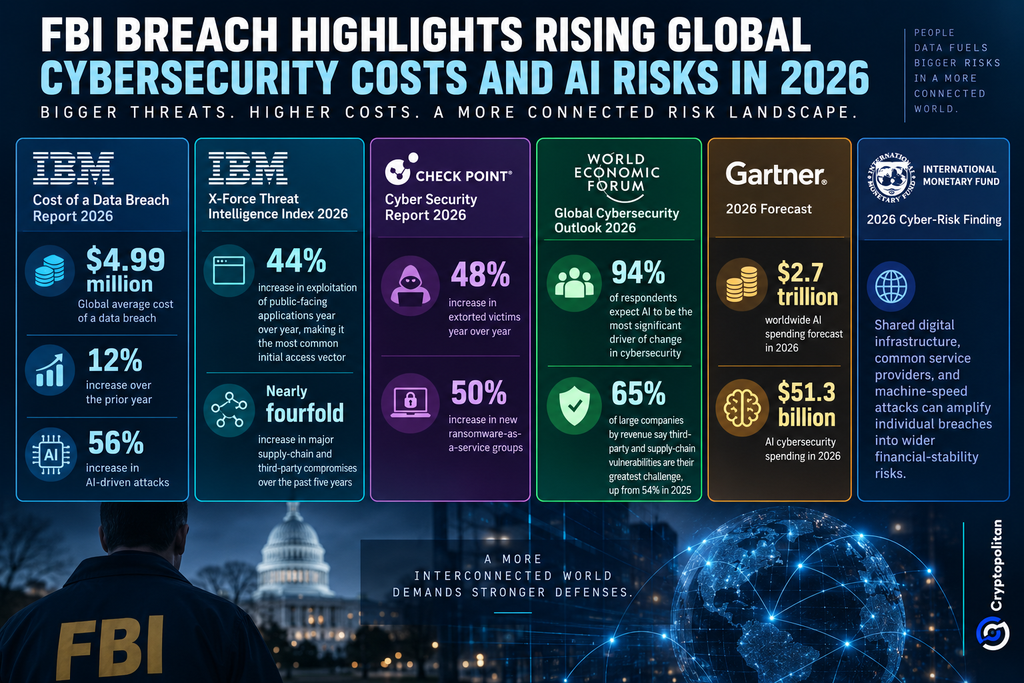 FBI breach highlights rising global cybersecurity costs and AI risks in 2026
The pressure is becoming structural. Check Point recorded a 48% rise in extortion victims, while the World Economic Forum found 94% of respondents expect AI to be the biggest force reshaping cybersecurity. Gartner forecasts $2.7 trillion in worldwide AI spending in 2026, while the IMF warns that shared digital infrastructure and machine-speed attacks can turn individual breaches into broader financial-stability risks.
If you're reading this, you’re already ahead. Stay there with our newsletter.

 English (US)